Knowledge that
builds trust.
Insights on audit, compliance, cryptography, and immutable infrastructure.
Explore articlesFrom theory to
technical decisions.
Explore the foundations and choices behind auditable, secure, and trustworthy systems.
 Latest article
Security Detection Without a SOC: Catching Brute Force, Suspicious Logins, and Privileged Abuse Early
Small and mid-sized software companies can't run a 24/7 SOC or an enterprise SIEM, but they can still catch the attacks that matter most. Here is how detection actually works and what it does and doesn't cover.
Privileged Access Monitoring for SaaS Teams: Watching the People Who Can Watch Everything
Admin and root accounts are the most powerful in your system, and the least monitored. Here is how to reconstruct who changed what, why a mutable log can't fully answer that question, and where detection and audit connect.
What Your Logs Aren't Telling You: Event Observability for Small Engineering Teams
Small and mid-sized engineering teams don't have a compliance problem, they have a scattered-logs problem. Here is why event visibility has to come before detection or proof, and what a single searchable stream actually buys you.
When a Log Becomes Evidence: What Strengthens a System Record's Evidentiary Integrity
Not every log record survives serious scrutiny. Courts, arbitrators, and regulators evaluate evidence differently from engineering teams. Here is what strengthens a system record's evidentiary integrity, not a guarantee of admissibility, but a meaningfully stronger position.
LGPD in Practice: What the Law Actually Requires From Your Audit Logs
Brazil’s data protection law requires more than storing records. It requires that you can demonstrate what happened to personal data, when it happened, and who was involved. Most logging systems cannot do that reliably.
Future-Proofing Your Systems: Why Event Integrity Matters
AI, automation, and digital disputes are turning mathematical proof of events into a competitive requirement. Here’s why integrity must be built into the foundation.
The Day a Regulator Asks: "Can You Prove This Event Happened?"
Observing and logging get you most of the way there. Proof is the layer that carries you the rest, when the stakes are highest. Here is what changes when explanation is no longer enough.
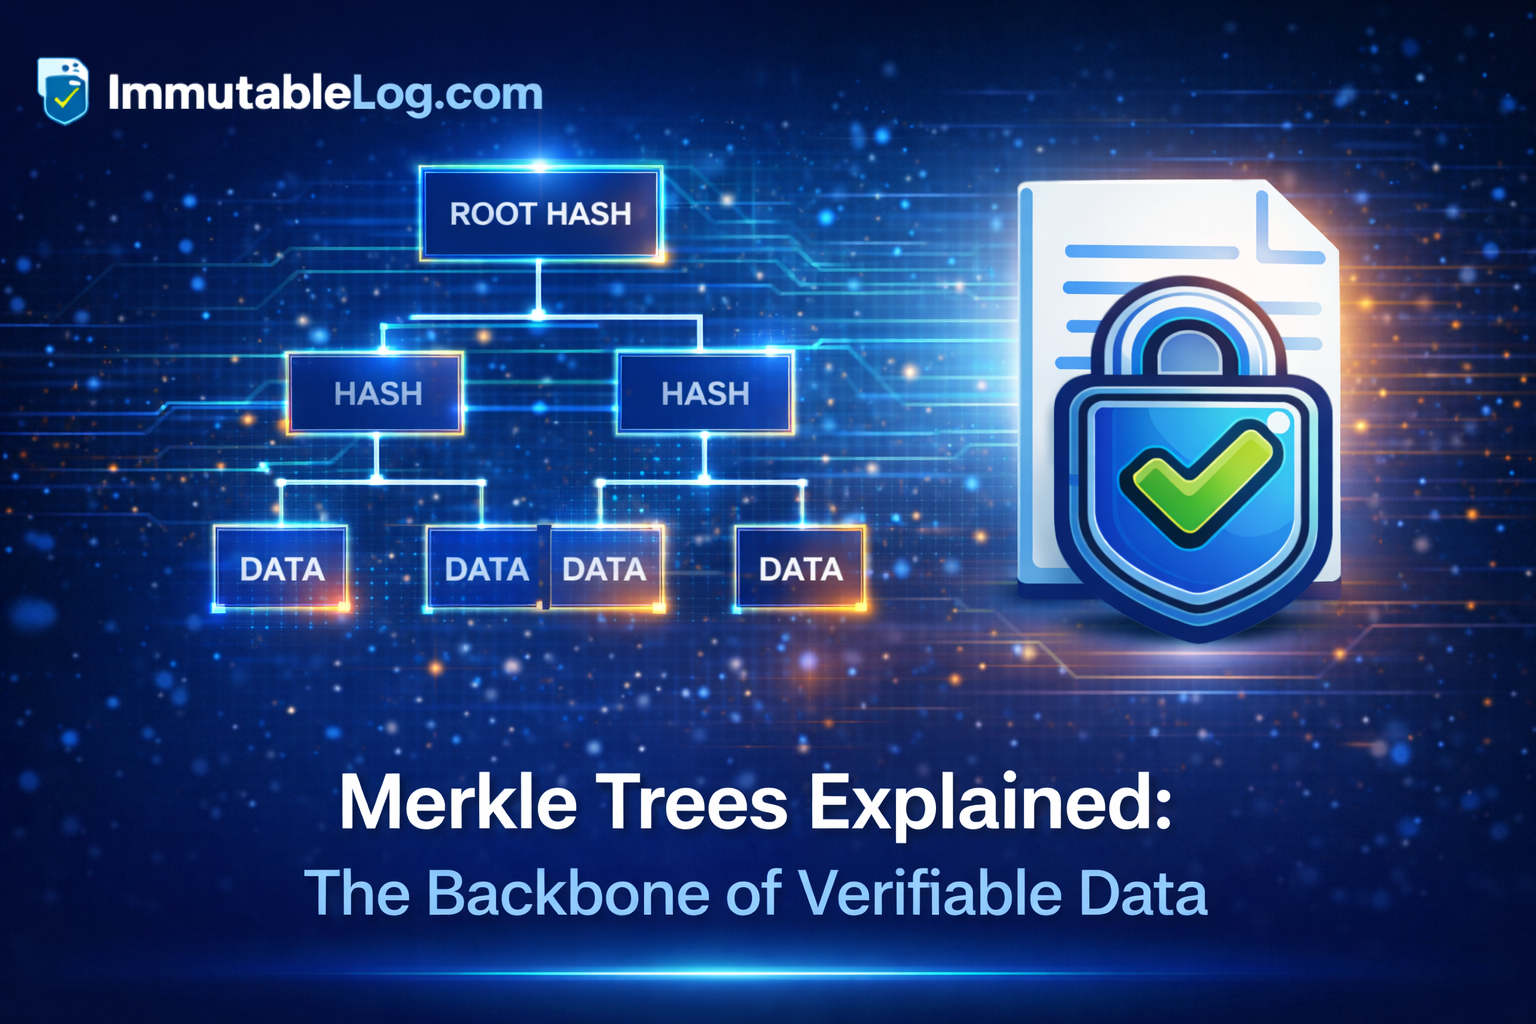
Merkle Trees Explained: The Backbone of Verifiable Data
Merkle trees make it possible to prove that a specific event belongs to a dataset without exposing everything else. Here’s why that matters for enterprise audit trails.
The Hidden Risk of Mutable Systems
Mutable logs create silent risk for fraud, insider abuse, and dispute resolution. Integrity needs to be built into your systems from day one.
How Tamper-Evident Logs Strengthen Compliance (SOC 2, ISO 27001, PCI DSS, LGPD)
Verifiable logs reduce audit risk across SOC 2, ISO 27001, PCI DSS, and LGPD. Here’s how tamper-evident records align with each framework’s compliance expectations.
How Cryptographic Hashes Create Trust in Data
A single bit change breaks verification instantly. Here's how cryptographic hashing turns tamper detection into a mathematical guarantee.
Blockchain vs Immutable Ledgers: What’s the Real Difference?
ImmutableLog is not crypto and not a public blockchain. But it delivers blockchain-grade integrity for enterprise systems. Here’s what that actually means.
The Problem You Only Discover During an Audit
Most companies only discover their log integrity gap when a regulator, auditor, or enterprise customer asks for proof. By then, the historical record cannot be fixed.
Observability, Detection, Audit, and Proof: How the Four Layers Fit Together
Observability tells you what your system is doing. Detection tells you when to look. Audit gives you a trail. Proof gives that trail a cryptographic guarantee a stranger can verify. Here is how the four layers build on each other.
Why Traditional Logs Cannot Be Trusted in Critical Systems
Traditional logs help teams debug and investigate. But they cannot provide proof. Here is why mutable logging systems fail when integrity matters most.
Turn knowledge
into trustworthy records.
Explore the integration or discuss the security and audit challenges of your operations.